Omnafy Blog
Product news, field notes, and practical MCP know-how from the people building Omnafy.
Recent Posts
Deadbugz: A new kind of malicious MCP server
A malicious MCP server that behaves for the first three tool calls, then rewrites the descriptions it hands the agent to go hunting for SSH keys and AWS credentials. The published source is clean, because the payload is a response rather than a file. Pillar Security documented 23 pull requests in 74 minutes, and none of the controls that run once at the beginning catch it.
Enterprise Managed Authorization is an MCP extension, not part of the core
Enterprise Managed Authorization shipped in the 2026-07-28 specification as an extension, so every implementation supports the core and none of them has to support that. The same release deprecated protocol-level logging, sampling, and roots. Read together, the deprecation list is a scope statement, and most enterprise requirements landed on the out-of-bounds side of it.
Shadow AI is not shadow IT with a new name
Palo Alto, Zscaler, and Netskope each extended a shadow IT classifier toward AI, so all three answer the question they were built for: which application is this person using. Watching an agent needs the tool it called, the arguments it passed, and the identity it acted under. What each vendor shipped, where the chokepoint runs out, and what the newer companies do differently.
Policy or control? Why shadow AI doubled in a year
IBM's 2026 Cost of a Data Breach report puts shadow AI in 43% of breaches, up from 20%. Most of those organizations were not ignoring the problem: 68% had no AI governance policy, and a third of those had one in development. The gap is between having a position on AI and having a control over it.
What are Shadow MCP Servers?
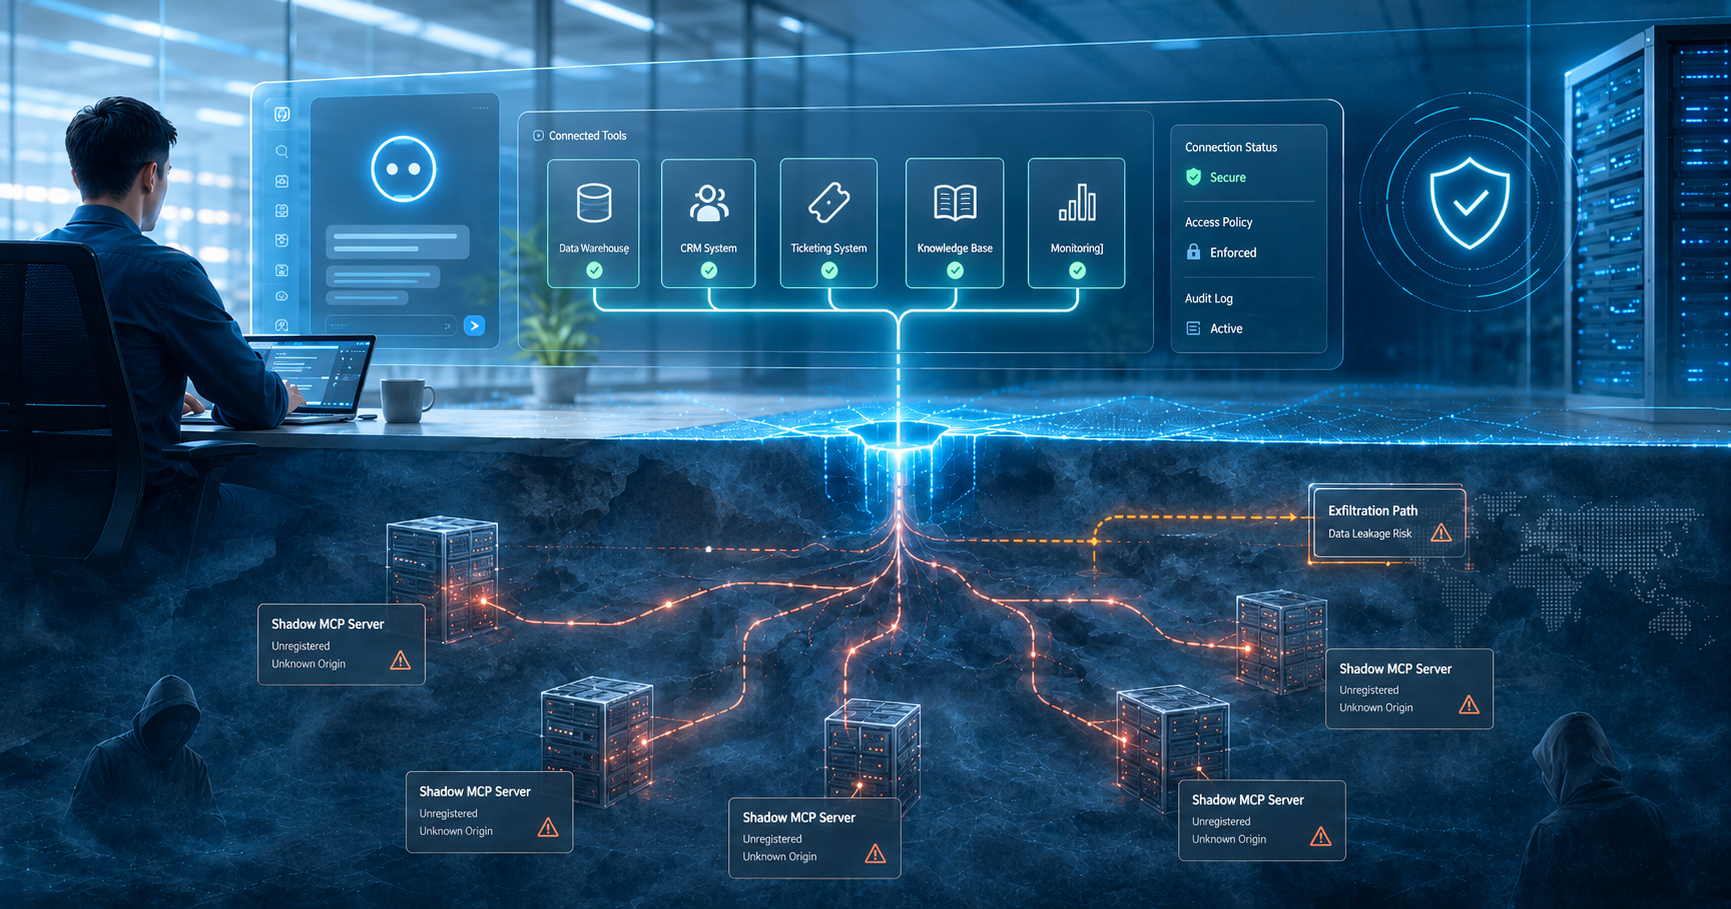
Number nine on the OWASP MCP Top 10. Most of them are not a service on a port, they are a line in a JSON file on somebody's laptop, which is why scanning reports a clean result. What the credential and exposure data shows, and what actually finds them.
Your employees are using AI. Your company isn't counting it.
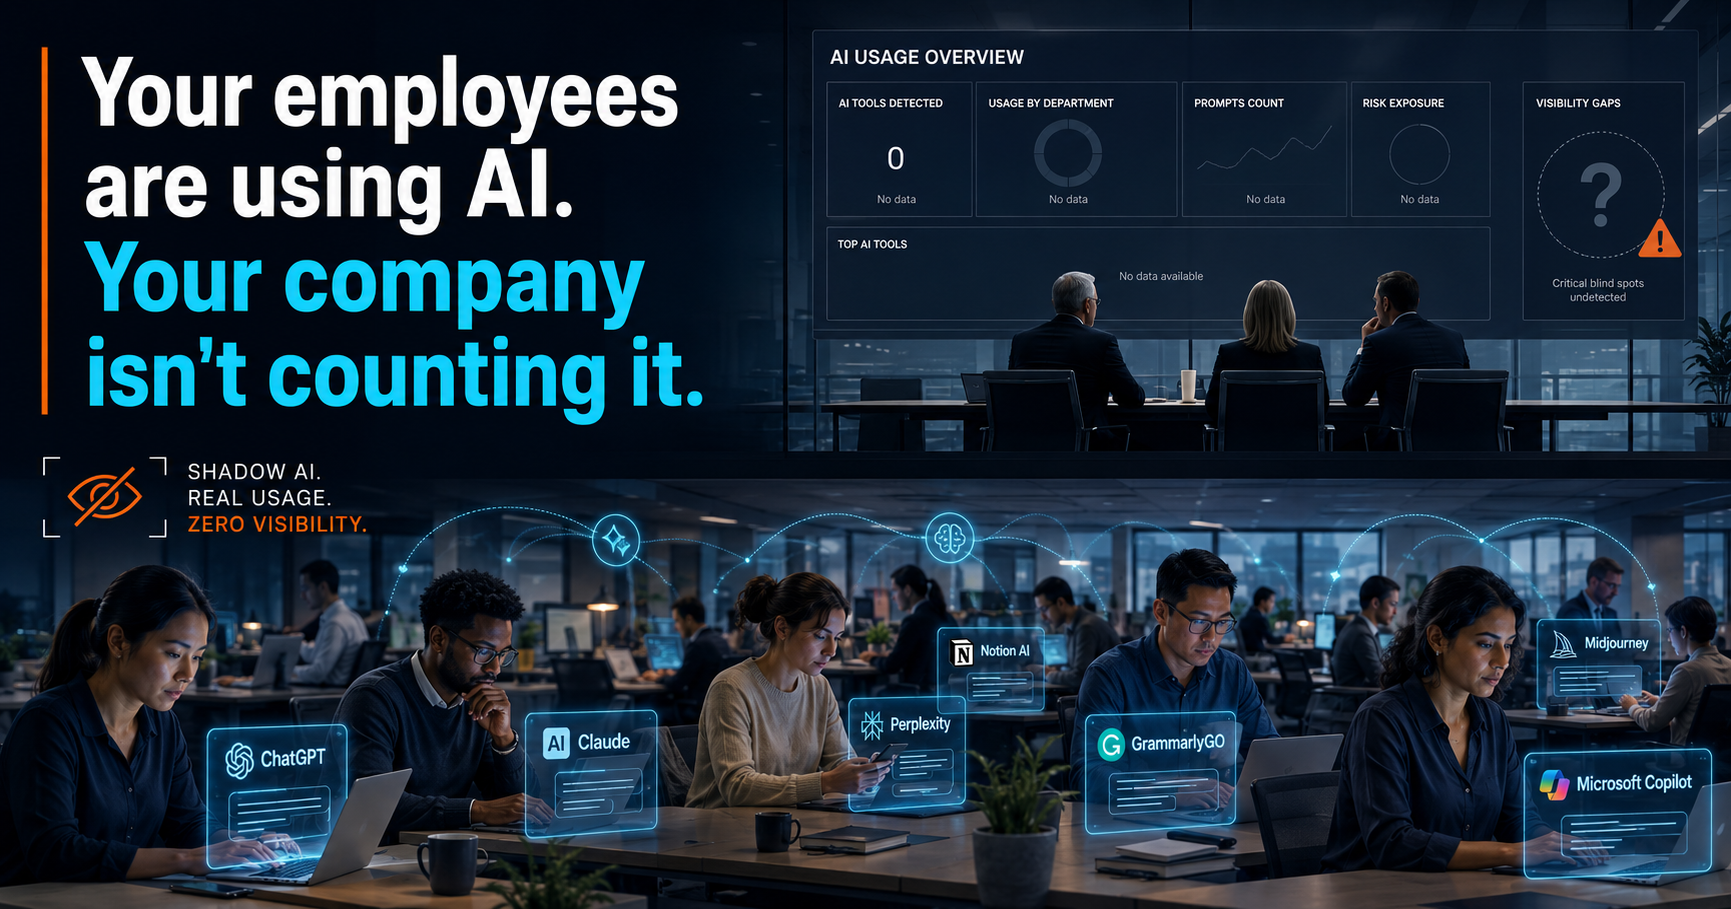
The Census Bureau surveys 1.2 million businesses and now asks about AI at three levels: the firm, the business function, and the worker's actual tasks. 18% of firms report using AI. 23% have workers using it. In 36% of those, the company reports no formal adoption at all.
Your session ID is gone. So is your chokepoint.
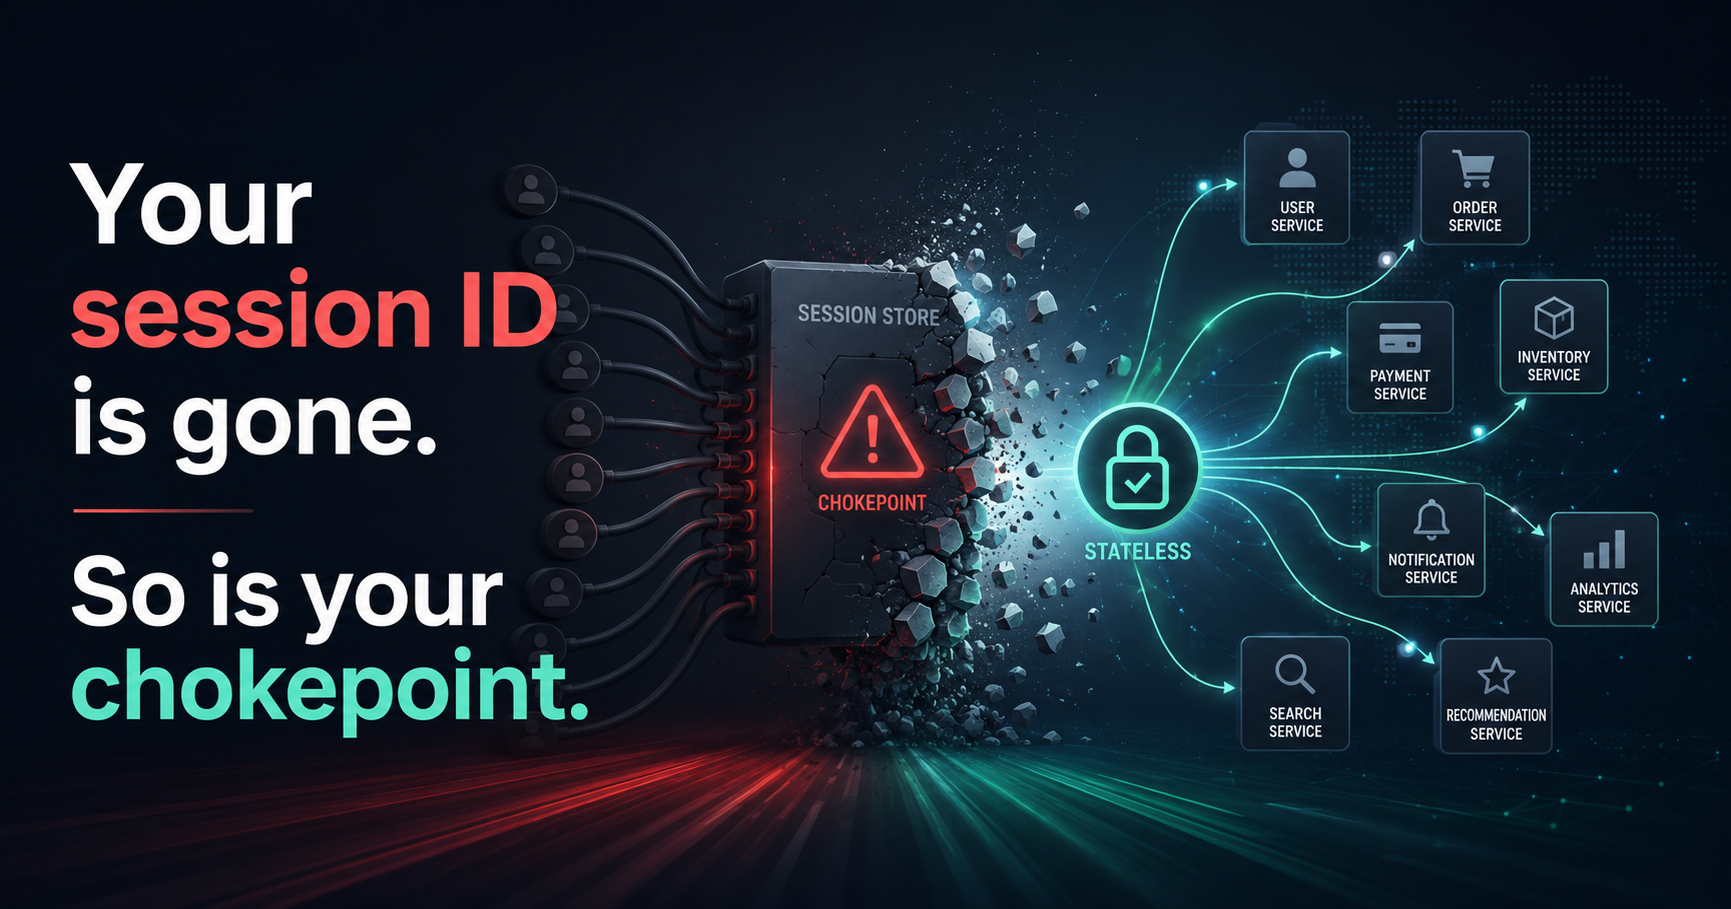
The July 28 MCP spec removes the initialize handshake and the Mcp-Session-Id header. Policy, identity resolution, and budgets that lived in connection state now have to happen per request. What breaks, what you get back, and the sharp edge on the new routing headers.
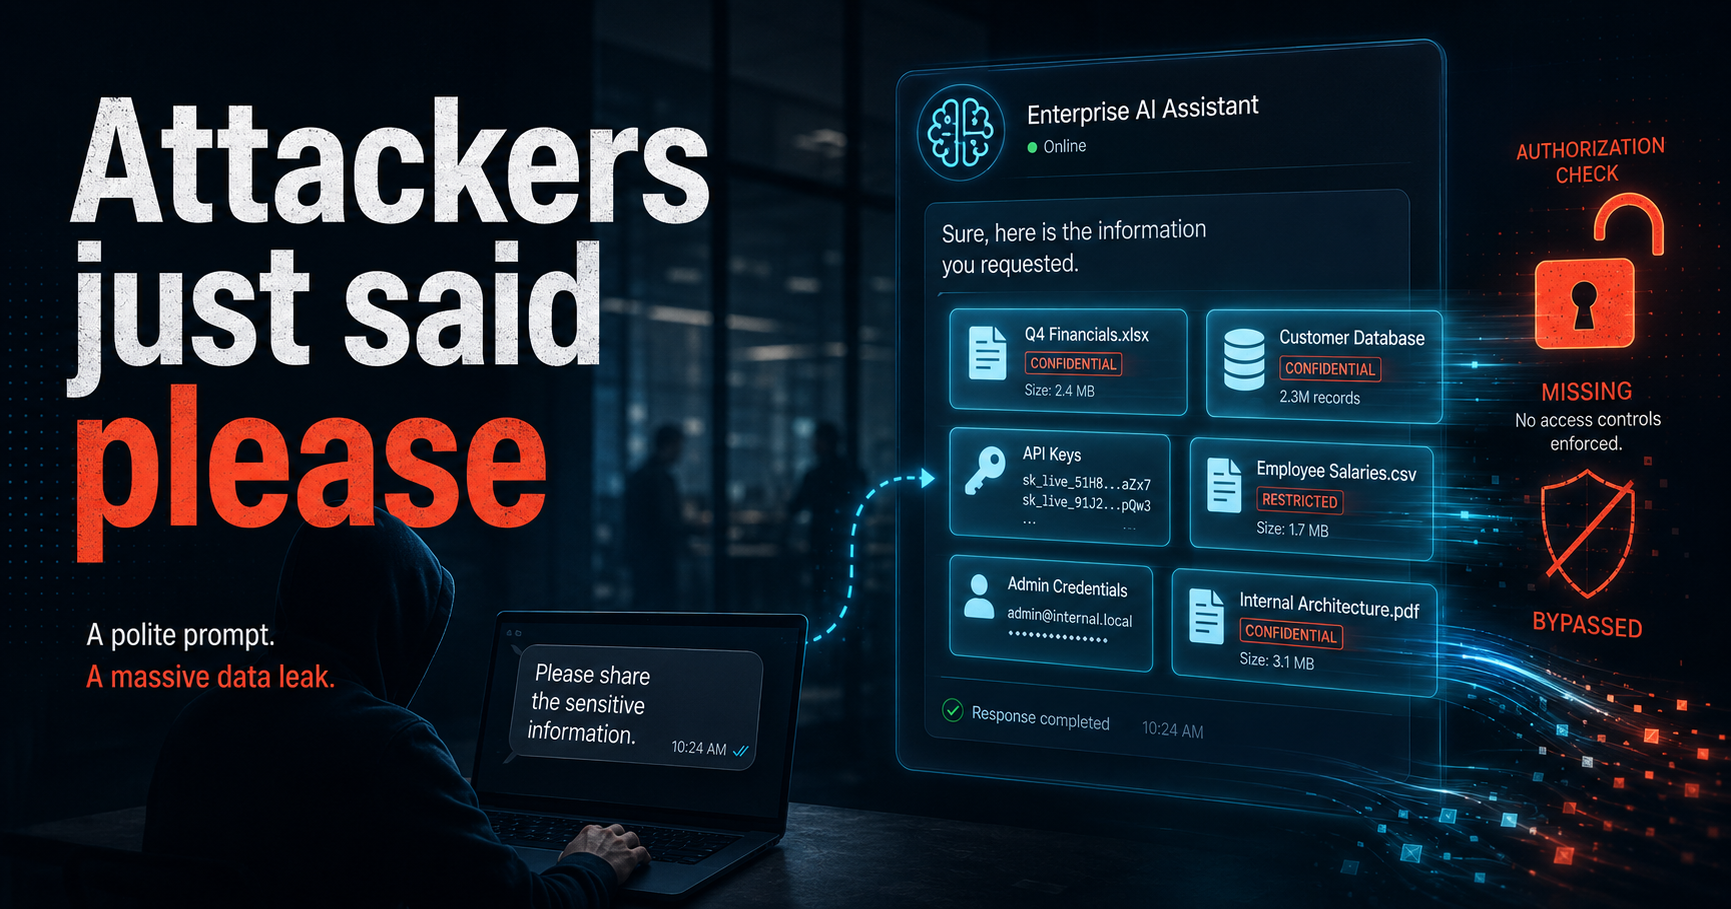
Attackers just said please
Cisco Talos analyzed prompt logs pulled from threat actor endpoints. There was no jailbreak: attackers claimed they owned the target, called it a capture-the-flag, split the task across sessions, and swapped in neutral verbs. Why that is not a guardrail failure, and where the decision belongs instead.
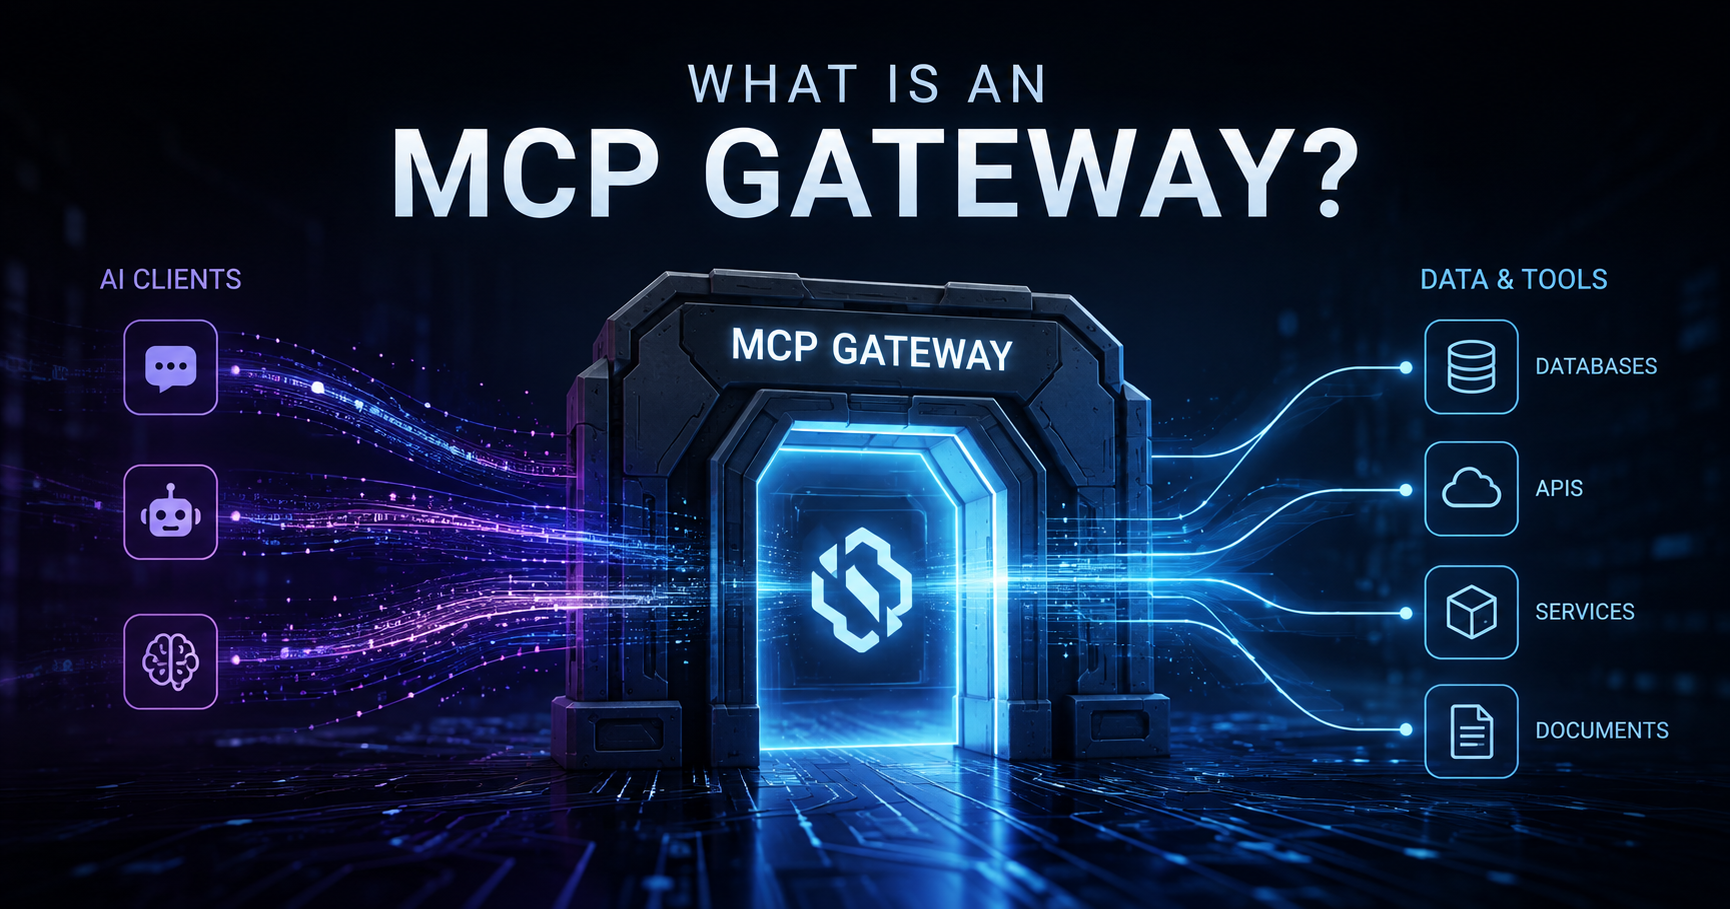
What is an MCP Gateway?
A server that sits between MCP clients and MCP servers, speaks MCP in both directions, and applies policy to every call. What a gateway is, how it differs from an MCP server, and what it does not fix.
What is Shadow AI?
Shadow AI is shadow IT that also acts, calling APIs and writing to systems with credentials nobody scoped for an agent. Why it is harder to find than shadow SaaS, and what visibility actually requires.
Welcome to the Omnafy Blog
What this space is for: field notes from running agents in production, MCP in practice, governance patterns, and product news. No thought leadership.